If you’re a CISO or security leader, you’re probably fielding questions about AI governance from every direction. Stakeholders want to understand risk exposure, finance teams are trying to predict AI spend, and legal staff are tracking a growing list of AI regulations. Meanwhile, business units are pushing to deploy AI capabilities as quickly as possible, and employees are already using applications (whether they’re sanctioned or not).
For security teams, the pressure is on. Figuring out how to support AI adoption without inviting unacceptable risk might feel like you’re laying the track in front of a moving train. AI governance platforms are designed to ease this pressure.
In this guide, we'll talk about why organizations are using AI governance platforms, the capabilities that really matter, and our assessment of leading applications on the market today.
Why are organizations investing in AI governance platforms?
Risk and regulation are driving adoption.
As AI adoption spikes, many companies are actually growing less confident in their ability to manage risks, according to research by McKinsey. One of the reasons AI creates anxiety is because there’s a lack of clarity about who’s accountable for what it does. Another pressure comes from growing regulatory requirements. Just a decade ago, there were no AI-related laws among G20 countries. Between 2016 and 2025, the US has passed 25 AI-related bills in the G20 dataset, and in Europe, the landmark EU Artificial Intelligence Act is already in force. As Deloitte notes in its 2026 State of AI in the Enterprise report, “the AI risks companies are most worried about all relate to governance.”
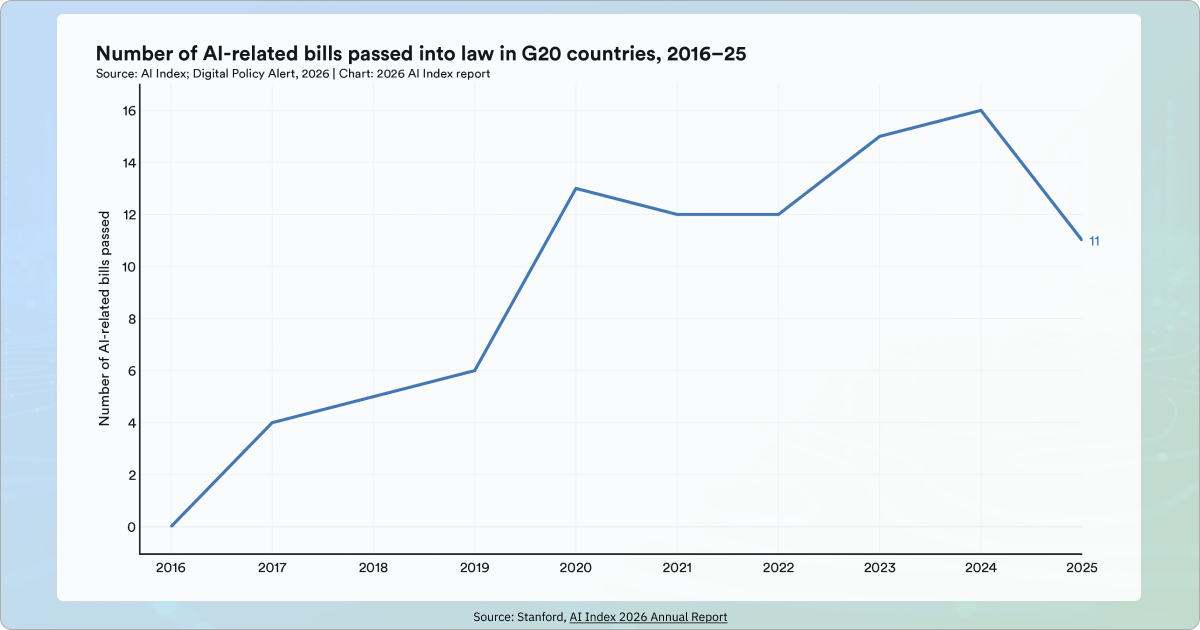
To navigate this tangle, a growing number of organizations are investing in new resources: AI governance job postings increased 17% last year, and many companies are now relying on specialized platforms to support AI governance. Below is a list of the top AI governance concerns reported by leaders, according to Deloitte.
AI Governance Concerns
Regulatory Compliance
Regulations are already in force, with more coming. The EU AI Act’s requirements on prohibited AI practices, general-purpose AI models, and transparency are already in force, with rules for high-risk systems phasing in through 2028. US states like California and Colorado have enacted their own AI laws. Many enterprises will soon face requirements for documentation, impact assessments, and human oversight mechanisms, if they don’t already.
Shadow AI
You can’t govern what you don’t see. As employees deploy tools, connect APIs, and spin up agents without IT knowing, risk increases. Every AI system that’s not inventoried is outside the governance framework, and that opens the door to irreparable damage.
Sensitive Data Exposure
AI tools process whatever employees put into them. Without controls at the prompt and response layer, confidential documents, customer records, financial data, and intellectual property flow to external model providers with no organizational visibility and no ability to intervene. Most traditional DLP tools were not designed to scan conversational AI interactions, leaving a gap that grows with every new AI tool in use.
Policy Fragmentation
It’s common to see different AI tools and different risk appetites across different functions, with no central policy oversight. Finance may have informal guidelines; legal may have different ones; engineering may have none. Every new model in use expands your attack surface and further fragments policies.
Third-Party AI Risk
Every AI-powered SaaS product, every model accessed, and every vendor embedding AI into their service delivery is a source of inherited risk.
Accountability Gaps
When an AI system causes harm, the first questions are what happened and who was responsible. Without documented governance processes and audit trails, there’s no evidence that appropriate oversight ever existed. That’s a legal and regulatory problem, not just an operational one.
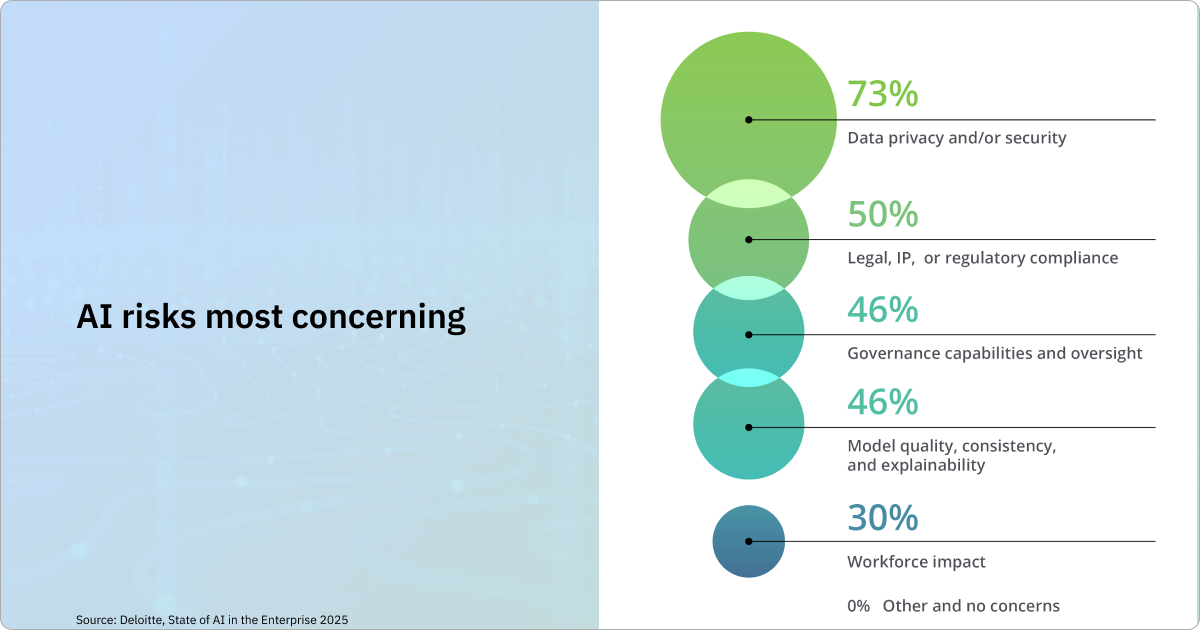
Source: Deloitte, State of AI in the Enterprise, January 2026 (survey conducted in 2025).
Features to look for in an AI governance platform
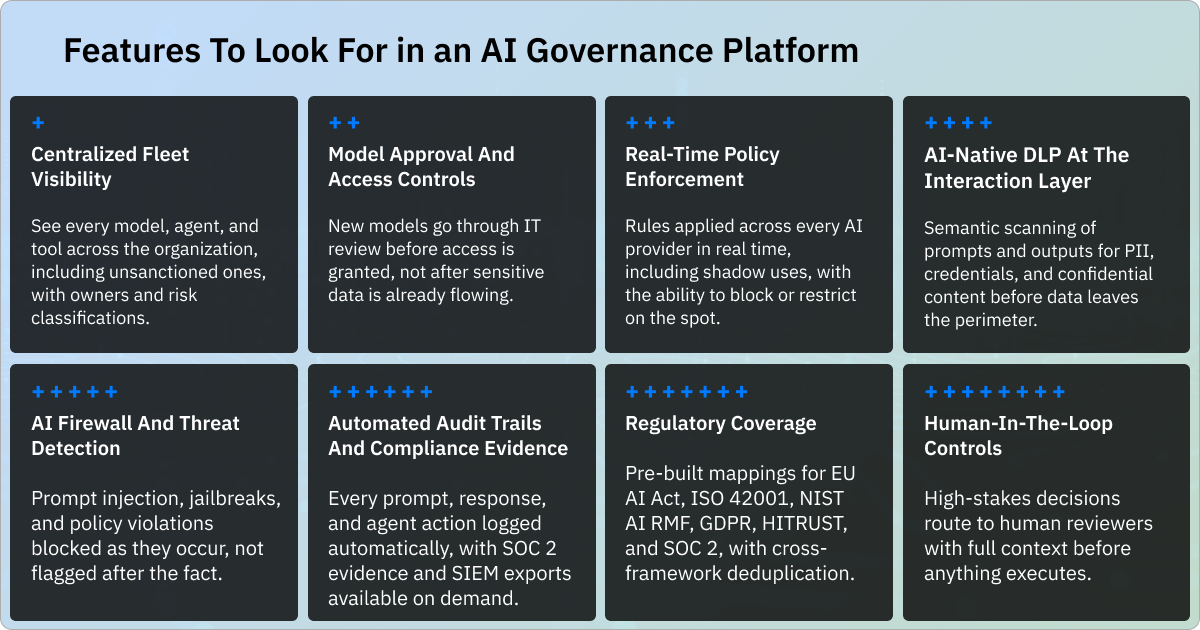
Not all AI governance platforms are built for the same purpose. Some enforce policy, others focus on documentation and audit readiness. Before you weigh different options, it’s a good idea to make sure you’re clear on your needs. Are you looking for real-time control? Regulatory compliance? AI inventory and auditing? Or all three? Regardless of your priority, there are a handful of essential capabilities your platform should provide. Here’s our assessment of the features that really matter:
1. Centralized Fleet Visibility
To govern AI, you need to see how different applications are being used in your organization, including unsanctioned ones. Your platform should provide visibility across the models, agents, third-party tools, and embedded AI features it supports. You should see owners, use cases, and risk classifications. Ideally, you’ll have a centralized space where you can observe agents executing tasks, inspect their execution traces and tool calls, and intervene if needed.
2. Model Approval and Access Controls
AI models should go through a thorough approval process before employees can use them. IT teams need to review security posture, data-handling practices, and residency before a model is granted access, not once it’s already processing sensitive data. One way to streamline this is by bringing all the apps into one secure productivity workspace, with governance built in.
3. Real-Time Policy Enforcement
You should be able to enforce rules in real time across the AI providers and access paths it supports, including governed controls for shadow uses. Your platform should allow you to block sensitive data categories, restrict access to unsanctioned tools, and require business justification for certain interactions.
4. AI-Native DLP at the Interaction Layer
Look for a platform that analyzes AI behavior and intentions, instead of just scanning for known patterns. Traditional DLP recognizes fixed signatures. But AI threats change their wording, hide inside legitimate work, and move at machine speed.
5. AI Firewall and Threat Detection
Platforms should detect prompt injection, jailbreaks, adversarial manipulation, and policy violations as they occur rather than flagging them in post-incident review. Look for a tool that can block or route interactions based on policy rather than just logging them.
6. Automated Audit Trails and Compliance Evidence
Relevant interaction metadata, agent actions, tool invocations, and policy enforcement outcomes should be recorded automatically with enough detail to support audits. You should be able to generate SOC 2 evidence, compliance exports, and SIEM feeds on demand, without manual reconstruction.
7. Regulatory Coverage
For streamlined compliance, look for pre-built control mappings for frameworks like the EU AI Act, ISO 42001, NIST AI RMF, GDPR, HITRUST, and SOC 2.
8. Human-in-the-Loop Controls
You should have configurable autonomy levels that route high-stakes AI decisions to human reviewers before they execute. Your platform should surface the available decision context (data sources, confidence information when available, and the proposed action).
The 5 Best AI Governance Platforms in 2026
The market for AI governance tools is still maturing. Providers offer a range of solutions, from compliance and auditing tools to real-time enforcement layers. Before choosing a tool, it’s helpful to get clear on the most pressing problem you’re trying to solve. Below, we provide an overview of features offered by leading platforms on the market (in no particular order).
Credo AI
Credo AI organizes its architecture around the AI lifecycle. It aims to discover every AI system in the enterprise, assess it continuously against internal policies and external regulations, enforce governance workflows, and finally, generate documentation for auditors and regulators.
The company uses a centralized inventory system to cover models, agents, and applications. Its risk assessment workflows use AI-specific risk scenarios (e.g., hallucination, drift, bias, agent behavior) rather than generic risk categories. Credo AI users have access to pre-built policy packs covering the EU AI Act, NIST AI RMF, ISO 42001, SOC 2, and other standards. Credo provides automated evidence generation and cross-functional collaboration tools that are designed to bring legal, compliance, security, and engineering teams into a shared workflow. Its Govern AI Assistant adds agentic compliance workflows to the platform.
Best for: Enterprises in regulated industries that have a significant AI portfolio and compliance demands and need dedicated, purpose-built AI governance infrastructure.
First Recon AI
First Recon AI takes a different approach to governance. Instead of adding a layer of oversight to the AI environment, First Recon is the AI environment; it’s a governed workspace where employees can engage safely with major AI models and agents, including ChatGPT, Claude, Gemini, Copilot, and other supported models.
This has a couple of practical outcomes. First, compliance evidence is generated automatically through normal workflows, not pulled together retroactively. Every enforcement decision leaves behind an audit record, with activity organized against the compliance frameworks configured for the organization. Compliance exports and SIEM integration make that evidence available to the external systems where it needs to go. You’ll have a sealed, metadata-only decision receipt for every enforcement decision. Instead of spending hours assembling evidence after you get a question from an auditor or your board, you can use records that already exist.
First Recon AI understands, secures, and proves every AI interaction (with any supported model) so your organization can adopt AI quickly. You can test out governance features through First Recon AI’s free 30-day trial.
Best for: First Recon is a good fit for enterprises of all sizes and sectors where AI is already in use across multiple providers. It supports rapid AI adoption: organizations get governance and compliance evidence built into their AI operating environment from the start, rather than applied as a separate layer after the fact.
Palo Alto Networks: Prisma AIRS
Palo Alto Networks sits at the intersection of AI security and compliance documentation. The company's AI governance framework emphasizes comprehensive AI model inventories, policies for sanctioned and unsanctioned models, data poisoning prevention, model vetting and approval before deployment, continuous monitoring for anomalous behavior, and regular audits to ensure compliance.
Prisma AIRS operationalizes parts of this through AI asset discovery and inventory, with metadata about models, agents, endpoints, datasets, cloud accounts, and asset relationships. This can support documentation needed for regulatory frameworks like the EU AI Act.
Integration with Cortex Cloud AI-SPM provides asset discovery, posture analysis, and data classification for training datasets across onboarded cloud accounts. The Portkey acquisition adds a centralized AI Gateway that enforces consistent policies across models, logs token usage for cost attribution, and routes requests based on governance rules.
Best for: Organizations running Palo Alto Networks infrastructure that want AI governance integrated with their existing security stack, particularly where the primary governance need is AI inventory, policy enforcement, and audit logging of AI interactions.
Microsoft Purview
Microsoft's AI governance capabilities are embedded within its existing infrastructure, rather than delivered as a standalone platform. Microsoft Purview is the primary governance layer. It classifies sensitive data, monitors how it moves across AI tools and services, and enforces data handling policies at scale, with compliance reporting aligned to GDPR, HIPAA, and the EU AI Act.
Prompts and responses from Microsoft 365 Copilot and other integrated AI apps are captured in the unified audit log, with events showing how and when users interact with AI tools and which files were accessed during those interactions. For Agent 365, Purview supports auditing of agent-to-human, human-to-agent, agent-to-tool, and agent-to-agent interactions; records can include references to files accessed, but not a model’s private chain of thought.
Agent identities and access are managed through Microsoft Entra, while Purview applies audit, data security, and compliance controls to supported interactions.
Agent 365 acts as the control plane for observing, governing, and securing agents across Microsoft and other tools, with shared policies, security controls, and lifecycle oversight.
Best for: Enterprises already operating Microsoft 365, Azure, and the broader Microsoft security stack who want AI governance to extend naturally from existing compliance infrastructure rather than through a separate platform.
Noma
Noma's governance capabilities are embedded in a broader AI security platform, with a dedicated Governance and Compliance module that connects discovery, policy enforcement, and audit trail generation into a single workflow. The platform is designed to keep organizations audit-ready through real-time visibility, automated controls, and policy enforcement across the entire AI environment, mapping to frameworks like the EU AI Act. The recent launch of Agent Access Control added a dynamic Enterprise Agentic Registry that surfaces every agent, connected MCP server, and tool with context already attached. It shows what each server exposes, which agents connect to it, and where it stands against current security policies. This updates continuously in real time.
Each agent is assigned a distinct identity rather than operating under shared credentials, with governance states of Approved, Requires Review, or Blocked configurable per agent and MCP connection. The platform logs model activities, deployments, and security events for compliance and forensic analysis, with findings mapped to frameworks including ISO 42001, the EU AI Act, NIST AI RMF, MITRE ATLAS, and the OWASP LLM Top 10.
Best for: Enterprise security teams managing complex AI environments across multiple agent frameworks, MCP servers, and cloud platforms who need governance embedded in their security operations workflow.
Building a foundation before you scale
Our advice is to think of AI governance as the scaffolding you need for rapid scaling, not a blocker. It’s the foundation that lets you say yes to use cases, teams, and workflows without having to start a new conversation about risk each time.
Your ability to harness AI at scale will be shaped in large part by the governance system you put in place now. If you get that right, the pace of AI adoption will stop being a liability and will become an advantage.